MICROSOFT 365 IDENTITY SECURITY
Entra Conditional Access Quickstart
Reduce Microsoft 365 account compromise risk without rushing changes that could disrupt users or lock out administrators.
A fixed-scope service for SMEs that reviews your Microsoft Entra access controls, designs a practical Conditional Access and MFA baseline, validates emergency access and supports a safe, staged rollout.
Your trusted UK Microsoft consultancy.
What is an Entra Conditional Access Quickstart?
An Entra Conditional Access Quickstart is a fixed-fee Microsoft identity security service that reviews current access controls, designs a practical Conditional Access and MFA baseline, validates emergency access, tests agreed policies through report-only or pilot deployment and provides a clear operational handover.
It is designed for organisations that need stronger access security but do not want a rushed configuration exercise or a large enterprise transformation programme.
Know what is exposed, what matters most and what to fix first.
Microsoft 365 access is a business risk, not only an IT setting
Microsoft 365 often contains an organisation’s email, files, Teams conversations, SharePoint sites, finance communications and administrator controls. A compromised user or administrator account can therefore create financial, operational and information-security consequences.
The security features may already be available. The harder question is whether MFA, Conditional Access, privileged access and emergency access have been designed and applied consistently – without creating avoidable disruption.
MFA is enabled, but not reliably enforced
Users may be registered for MFA while important sign-in routes, exceptions or older configurations remain unclear.
Conditional Access policies are missing or difficult to trust
Policies may be absent, duplicated, overly broad, left in report-only mode or poorly documented.
Administrator access is overexposed
Too many people may hold privileged roles, or administrator accounts may be used for everyday work.
Emergency access is not operationally ready
Break-glass accounts may not exist, may be untested or may be included in policies that could cause lockout.
Legacy or exceptional access creates gaps
Older authentication methods, service dependencies, guest users or special cases can complicate enforcement.
Copilot and AI plans increase the need for strong identity
Before wider AI adoption, organisations need confidence that access decisions and privileged accounts are controlled.
Why Conditional Access matters
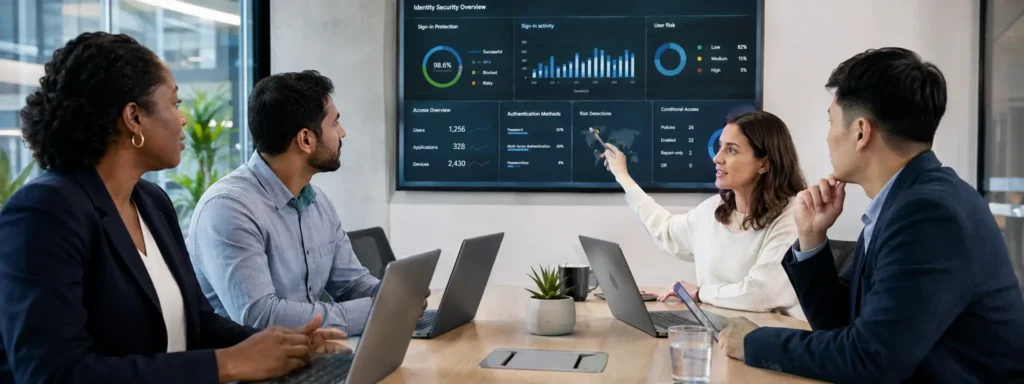
Microsoft Entra Conditional Access uses identity and access context to decide whether a sign-in should be allowed, blocked or subject to additional controls such as multifactor authentication. Used well, it provides a practical policy layer between a sign-in attempt and access to Microsoft 365 resources.
Used badly, it can create confusing exceptions, inconsistent protection or unexpected access failures. Stygian therefore treats Conditional Access as a controlled change programme: review first, design second, test before enforcement and retain a clear recovery path.
What the review Provides
- Microsoft Entra Access Baseline Pack
- Executive summary written for business and IT stakeholders
- Current-state identity and access findings
- Conditional Access baseline design summary
- MFA rollout approach
- Administrator hardening recommendations
- Emergency / break-glass access model
- Privileged-role, legacy authentication, guest access and sign-in observations
- Implementation summary showing what was configured, tested, enforced or retained in report-only mode
- Prioritised risk register and improvement backlog
- 30/60/90-day identity security roadmap
- Operational handover notes and a 60-minute walkthrough
Current-state access review
Review MFA status, existing Conditional Access policies, administrator roles, emergency access, obvious legacy authentication exposure, guest access considerations and recent sign-in observations.
MFA and Conditional Access baseline design
Design a practical policy baseline for the agreed tenant, including user coverage, administrator protection, exclusions, controls, policy state and rollout sequence.
Administrator protection
Identify obvious privileged-role exposure, excessive Global Administrator use and opportunities to separate everyday and administrative accounts.
Emergency access model
Review or define the emergency access approach, confirm relevant policy exclusions and document recommendations for secure use, monitoring and testing.
Report-only and pilot rollout
Configure agreed policies in report-only or pilot mode where appropriate, assess likely impact and capture required adjustments.
Controlled enforcement
Support one agreed wider enforcement wave where the evidence, emergency access position and client approval confirm that it is safe.
Risk-led handover
Provide a documented baseline, implementation summary, risk register, operational notes and a prioritised 30/60/90-day improvement roadmap.
MSP and internal IT collaboration
Work alongside the organisation’s existing IT team or MSP and provide documentation that supports ongoing administration.
The outcome: stronger access controls with a supportable operating position
Reduce account compromise exposure
Apply stronger authentication and access decisions more consistently across the agreed Microsoft 365 scope.
Protect privileged access
Give administrator accounts and roles clearer, stronger treatment than everyday user access.
Reduce lockout risk
Validate emergency access, exclusions, approvals and rollback before wider enforcement.
Create an evidence trail
Document the baseline design, approvals, changes, testing results and remaining risks.
Improve insurer and client assurance conversations
Provide practical evidence of access-control improvement, without claiming certification or guaranteed acceptance.
Prepare for wider Microsoft 365 and AI adoption
Build a more controlled identity foundation for future Copilot, device-compliance and governance work.
Unsure whether this review is the right starting point?
A short qualification conversation can determine whether the main requirement is a Microsoft 365 security baseline, a focused Entra access improvement, a Copilot data-exposure decision, a Power Platform governance issue or an active incident that requires a different response. Stygian will say when another service is the better fit.
Move from security uncertainty to a prioritised control plan
Get an evidence-led view of the Microsoft 365 risks that deserve immediate attention, the controls that need strengthening and the actions that can be sequenced over the next 90 days.
Why Choose Stygian?
Turn Microsoft 365 configuration into a defensible business-risk decision
Stygian combines cybersecurity, business architecture and Microsoft 365 consulting discipline. The review does not begin and end with a product score. It connects technical evidence to operational impact, leadership priorities, available Microsoft capabilities and a realistic improvement sequence.
Cybersecurity-led judgement
The service is framed around account compromise, privileged access, operational disruption and supportable control - not configuration for its own sake.
Designed for SME reality
The approach is bounded, remote-first and practical for organisations that cannot absorb a large enterprise identity programme.
Safe, staged implementation
Approval gates, report-only evaluation, pilot testing, emergency access validation and rollback planning reduce avoidable rollout risk.
Independent quality challenge
Higher-risk designs and enforcement decisions can be independently reviewed rather than relying on one person to design and approve the same change.
Works alongside your MSP or IT team
Stygian can provide specialist Entra support while the existing MSP or internal IT team retains the wider support relationship.
Clear handover and next steps
The client receives usable documentation, operational notes and one prioritised next-step recommendation.
What is not included
The Quickstart is deliberately focused on Microsoft Entra identity and access controls. It is not positioned as a complete Microsoft 365 security programme.
- Full Microsoft 365 security audit or broad tenant-hardening programme
- New Intune deployment, device enrolment remediation or endpoint migration
- Microsoft Defender, Sentinel, SOC or incident-response services
- Microsoft Purview, DLP, retention or information-governance implementation
- SharePoint, Teams or OneDrive permissions clean-up
- Privileged Identity Management implementation or full access-review programme
- Full joiner, mover and leaver process redesign or HR integration
- Penetration testing, formal certification or a guarantee of cyber-insurance acceptance
Where wider risks are identified, they are recorded and prioritised rather than absorbed into the fixed scope without agreement.
Frequently asked questions about the Microsoft Entra Conditional Access Review
What is Microsoft Entra Conditional Access?
Microsoft Entra Conditional Access is a policy capability that evaluates sign-in context and applies access decisions such as requiring multifactor authentication, restricting access or blocking a sign-in. The design must reflect the organisation’s users, applications, exceptions and operating needs.
Is enabling MFA the same as enforcing MFA?
No. Users may be registered for MFA without every relevant sign-in being consistently governed. The Quickstart reviews the current position and designs a more controlled enforcement approach through Conditional Access.
Do you make changes in our Microsoft 365 tenant?
Yes, where this is agreed in scope. Stygian provides assisted implementation of the approved baseline. Material configuration and enforcement decisions require client approval and are recorded through change control.
Could Conditional Access lock users or administrators out?
Poorly planned policies can disrupt access. The Quickstart is specifically designed to reduce this risk through emergency access validation, exclusions, report-only evaluation, pilot testing, approval gates and rollback notes.
What Microsoft licensing is required?
Conditional Access generally requires Microsoft Entra ID P1 for affected users. This capability is included in Microsoft 365 Business Premium and Microsoft 365 E3, while other licensing combinations may also apply. Stygian confirms licensing suitability during qualification.
Is Microsoft Intune included?
The Quickstart can consider existing Intune compliance signals where they are already configured and reliable. New Intune deployment, compliance-policy creation and device remediation are separate services.
Is this a full Microsoft 365 security assessment?
No. This is a focused identity and access service covering Entra, MFA, Conditional Access, administrator protection, emergency access and related access observations. A broader Microsoft 365 Security Baseline Review is available separately.
Can Stygian work with our existing MSP or IT provider?
Yes. The service can be delivered alongside an existing MSP or internal IT team, with responsibilities, access and approvals agreed before work starts.
Will the service guarantee cyber-insurance approval?
No. The Quickstart can provide evidence of practical access-control improvement, but acceptance depends on the insurer’s wording, evidence requirements and underwriting decision.
How long does the Quickstart take?
SME Core is delivered over seven working days after readiness is confirmed. Enhanced scope is normally delivered over ten working days.
How are fees confirmed?
Final fixed fees are confirmed after qualification based on user numbers, tenant type, existing policies, stakeholder availability and rollout complexity.
What happens after the Quickstart?
The client receives a prioritised roadmap. Where higher-priority actions remain, the usual next step is an Identity Hardening Sprint. Where ongoing oversight is required, Stygian may recommend a Managed Identity Security Retainer.
Any Questions You Want to Ask?
Have questions about the Microsoft Entra Conditional Access, access requirements or whether the service fits your current concern? Speak to Stygian before committing to a wider audit or remediation programme.
Turn Microsoft 365 security uncertainty into a practical priority
Before adding more users, licences, external collaboration or AI capabilities, establish where the material control gaps sit and what should happen first. Stygian provides a focused, independent review so leadership can prioritise action with a clear evidence base.
Are your Microsoft 365 access controls strong enough - and safe to enforce?
Book a focused call to confirm whether the Entra Conditional Access Quickstart is the right fit for your tenant.
Blogs and Insights
AI Assurance Shouldn’t Be a Final Gate
The UK’s new AI Risk Management Toolkit points towards a better model: continuous AI assurance tied to services, architecture and real-world outcomes.
Legacy Is a Risk Problem, Not an Age Problem
GDS is rethinking the Service Standard around whole services. That should change how architects think about technology, operations and service outcomes.
Good Services Don’t End at the Digital Boundary
GDS is rethinking the Service Standard around whole services. That should change how architects think about technology, operations and service outcomes.