MICROSOFT 365 SECURITY ASSESSMENT
Know what is exposed, what matters most and what to fix first
Microsoft 365 often becomes the operating system of a growing business before its security controls are reviewed as a whole. Identity, administrator access, devices, email, Teams, SharePoint, OneDrive and data protection can develop at different speeds, leaving leadership without a reliable view of the most important gaps.
Stygian’s Microsoft 365 Security Baseline Review gives UK SMEs and lower mid-market organisations a fixed-scope, independent way to understand their current control position, identify high-risk weaknesses and agree a practical 30/60/90-day improvement plan. The review is assessment-only: we inspect, evidence and prioritise; any remediation is scoped separately.
Your trusted UK Microsoft consultancy.
What is a Microsoft 365 Security Baseline Review?
A Microsoft 365 Security Baseline Review is a structured, evidence-led assessment of the controls that protect identities, privileged access, devices, email, collaboration and business information. Stygian reviews the current position across ten defined control domains and turns the findings into a decision-ready scorecard, prioritised risk register and 30/60/90-day roadmap.
The service is designed for organisations with approximately 20–300 Microsoft 365 users and is normally delivered remotely over one to two weeks, depending on tenant size and complexity. It supports Microsoft 365 Business Standard, Business Premium, E3, E5 and mixed estates, with recommendations adjusted to the capabilities available.
Know what is exposed, what matters most and what to fix first.
Before growth or AI adoption increases the stakes, establish the security baseline
Microsoft 365 connects user accounts, email, files, meetings, devices and business applications. A weakness in one area can affect several others: a compromised identity may reach shared files; an over-privileged account may bypass normal controls; unmanaged devices may retain access to business information; and unclear ownership may leave alerts or leavers unresolved.
AI and Copilot adoption can make a clear baseline even more important. Microsoft 365 Copilot uses the access a user already has. It does not correct excessive permissions, weak identity controls or poor information governance. A proportionate security review helps leadership strengthen the foundation without turning the exercise into a full audit or an open-ended transformation programme.
MFA and access rules are inconsistent
Security defaults, Conditional Access and exceptions may have grown without a clear, tested design.
Administrator access is broader than necessary
Privileged roles, shared admin accounts or weak emergency-access arrangements increase the impact of compromise.
Joiner, mover and leaver controls rely on memory
Delayed account closure and inconsistent access changes can leave unnecessary permissions in place.
Device access is not consistently controlled
Personal, unmanaged or non-compliant devices may access company information without an agreed risk model.
Email protection is only partly configured
Built-in controls may exist, but anti-phishing, impersonation, Safe Links or Safe Attachments settings may not be used effectively.
Sharing has expanded without regular review
Guest accounts, broad groups, external links and old Teams or sites can create exposure that is difficult to see.
Licensed security capabilities are underused
The organisation may be paying for security, identity or device controls that have not been configured or operationalised.
Alerts exist without clear ownership
Security signals, audit information and recommended actions provide limited value if nobody is accountable for review and response.
What the review helps you understand
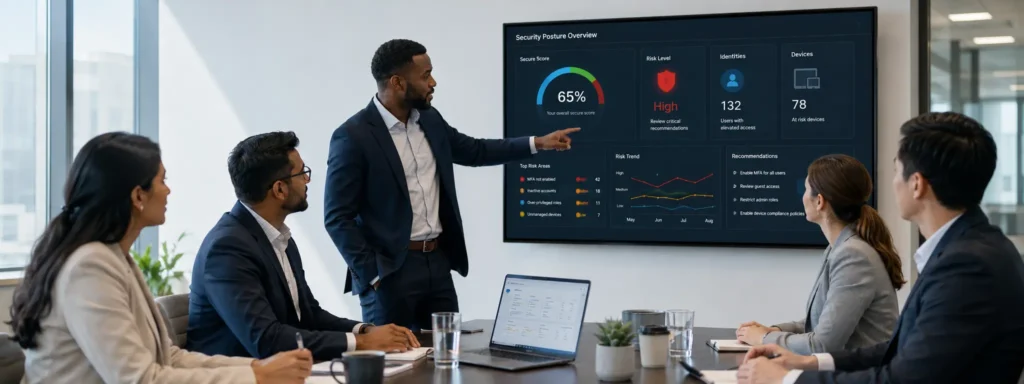
- Where identity, MFA and access-control weaknesses create the greatest exposure.
- Whether administrator roles and privileged operations follow a proportionate least-privilege model.
- Where joiner, mover and leaver processes could leave accounts or permissions active for too long.
- How managed, unmanaged and personal devices are allowed to reach Microsoft 365 data.
- Whether email and collaboration threat-protection settings are aligned with the organisation’s risk profile.
- Where SharePoint, OneDrive, Teams, guest access or external sharing require tighter ownership and control.
- Which Microsoft 365 data-protection, logging and alerting capabilities are available, configured and actively owned.
- Which licensed security capabilities are being used, underused or unavailable in the current licence mix.
- How the current baseline may affect safer Microsoft 365 Copilot or wider AI adoption.
- Which actions should be completed now, within 60 days and within 90 days – with owners and priorities made clear.
A prioritised control decision, not another generic audit
This service is designed to answer a specific leadership question: where are the material Microsoft 365 security gaps, which ones matter most and what should be addressed first?
The review is not a penetration test, compliance certification, incident-response engagement or exhaustive permissions audit. It also does not simply reproduce Microsoft Secure Score. Secure Score is used as one input, alongside configuration evidence, operational context, licence capability and risk-based sampling. The result is a practical business-risk view rather than a list of every possible Microsoft recommendation.
Because the engagement is assessment-only, Stygian does not make unapproved production changes during the review. Critical issues are escalated promptly, while remediation is authorised and scoped separately through appropriate change control.
Identity and authentication review
Assess account protection, MFA coverage, authentication methods and obvious identity-security gaps.
Conditional Access and access-control review
Examine how access is granted, restricted and excepted, including the practical use of security defaults or Conditional Access.
Administrator privilege review
Identify excessive privileged access, shared administrative practices and weaknesses in emergency-access arrangements.
Joiner, mover and leaver control review
Review how accounts and permissions are created, changed, disabled and checked when people move or leave.
Device security and endpoint-access review
Assess the controls governing managed, unmanaged and personal devices that connect to Microsoft 365.
Email and collaboration threat-protection review
Review anti-phishing, impersonation, malicious-link and attachment protections available within the client’s Microsoft 365 estate.
SharePoint, OneDrive and Teams sharing review
Examine tenant-level sharing, guest access, broad permissions and ownership risks using proportionate, risk-based samples.
Data protection and Purview basics
Review relevant information-protection, retention and data-loss-prevention capabilities at a baseline level, subject to licensing.
Logging, alerting and security-operations hygiene
Assess whether key signals are visible, reviewed and assigned to an accountable person or provider.
Security scorecard and risk register
Receive a clear view of control maturity, evidence confidence, business impact, severity, ownership and priority.
30/60/90-day improvement roadmap
Turn the findings into a sequenced plan covering immediate risk reduction, stabilisation and longer-term control improvement.
Leadership findings workshop
Use the final session to agree priorities, ownership and the appropriate next step rather than receiving a report without a decision.
Other Solutions
Microsoft Entra Access Baseline Review
Unsure whether this review is the right starting point?
A short qualification conversation can determine whether the main requirement is a Microsoft 365 security baseline, a focused Entra access improvement, a Copilot data-exposure decision, a Power Platform governance issue or an active incident that requires a different response. Stygian will say when another service is the better fit.
Move from security uncertainty to a prioritised control plan
Get an evidence-led view of the Microsoft 365 risks that deserve immediate attention, the controls that need strengthening and the actions that can be sequenced over the next 90 days.
Why Choose Stygian?
Turn Microsoft 365 configuration into a defensible business-risk decision
Stygian combines cybersecurity, business architecture and Microsoft 365 consulting discipline. The review does not begin and end with a product score. It connects technical evidence to operational impact, leadership priorities, available Microsoft capabilities and a realistic improvement sequence.
Business-risk led
Findings are explained in terms of exposure, operational impact and priority - not only technical configuration.
Fixed scope and evidence led
The review is time-bound, based on defined domains and supported by traceable evidence and stated limitations.
Independent of remediation
Stygian separates assessment from implementation so that the findings remain credible and production changes receive proper approval.
Cybersecurity and architecture foundation
Identity, devices, collaboration, data protection and operational ownership are considered as connected controls.
Works alongside your MSP or IT team
Stygian can provide specialist review capability without displacing the organisation’s day-to-day support relationship.
Clear next steps
Leadership receives a prioritised roadmap and one recommended next step rather than an unstructured list of technical recommendations.
Best suited to organisations that
- have approximately 20–300 Microsoft 365 users in one principal tenant;
- use Microsoft 365 Business Standard, Business Premium, E3, E5 or a mixed licence estate;
- want an independent view of security controls before growth, licence investment or AI adoption;
- have concerns about phishing, account compromise, administrator access, devices, sharing or leaver controls;
- are preparing for a cyber-insurance renewal, MSP handover, new IT leadership or board scrutiny;
- can provide an engaged business sponsor and an IT or MSP contact;
- can support read-only access, guided walkthroughs or proportionate evidence collection;
- want a controlled first step before committing to remediation or managed security support.
This service is not the right fit where
- there is an active or suspected compromise requiring incident response;
- the organisation requires penetration testing, Cyber Essentials certification, ISO 27001 audit or a formal compliance opinion;
- the requirement is only to implement a pre-defined set of changes;
- a complete file-level or SharePoint permissions audit is expected;
- a deep Microsoft Defender XDR, Sentinel, Purview or SOC assessment is required;
- multiple complex tenants, hybrid environments or more than 300 users are expected within standard scope;
- the client will not provide sufficient evidence or access to support credible findings;
- the expectation is that all weaknesses will be fixed during the assessment.
Frequently asked questions about the Microsoft 365 Security Baseline Review
What is a Microsoft 365 Security Baseline Review?
It is a fixed-scope, evidence-led assessment of the Microsoft 365 controls that protect identities, administrator access, devices, email, collaboration and business information. The review identifies material gaps and provides a prioritised 30/60/90-day improvement plan.
What areas of Microsoft 365 does the review cover?
The review covers ten domains: identity and authentication; Conditional Access; administrator privilege; joiner, mover and leaver controls; device security; email and collaboration threat protection; SharePoint, OneDrive and Teams sharing; data protection basics; logging and alerting; and licence capability usage.
Who is the review designed for?
It is designed primarily for SMEs and lower mid-market organisations with approximately 20–300 Microsoft 365 users, one principal tenant and a clear need to understand or improve their current security position.
How long does the review take?
Most reviews are completed remotely within one to two weeks after access, evidence and stakeholder availability have been confirmed. The exact timetable depends on tenant size, licence mix, complexity and the agreed package.
Do you need direct access to our Microsoft 365 tenant?
Read-only access is preferred for core administration and security portals because it improves efficiency and evidence quality. Guided screen-share, exports and screenshots can be used for sensitive areas or where temporary access is not appropriate. The access approach is agreed before work starts.
Is this the same as Microsoft Secure Score?
No. Secure Score is a useful input, but it is not a complete assessment and should not be treated as a guarantee against breach. Stygian combines relevant score recommendations with configuration evidence, operating context, licence capability, risk-based samples and business impact.
Is this a penetration test or compliance audit?
No. The service does not test applications or networks for exploitable vulnerabilities, certify compliance or provide a legal opinion. It is a baseline review of Microsoft 365 security configuration and operational control.
Does the review include remediation?
No. The review is assessment-only and does not include production changes. This protects scope, independence and change control. Stygian can provide a separately scoped remediation sprint, focused identity service or managed security retainer after the findings have been agreed.
Will the review help us prepare for Microsoft 365 Copilot or AI?
Yes, at a high level. The review considers whether identity, device, sharing, data-protection and governance gaps could weaken the foundation for safer AI adoption. It does not replace the deeper Microsoft 365 Copilot Readiness & Data Exposure Review where an active pilot or rollout decision is being made.
Can Stygian work with our existing MSP or internal IT team?
Yes. The review is designed to complement internal IT and managed-service providers. They can support evidence collection, technical validation and follow-on action while retaining the day-to-day support relationship.
How are the fees calculated?
The review is provided on a fixed-fee basis. The fee depends on the agreed package, user count, tenant complexity, licence mix, evidence approach and any additional sampling or briefing requirements. The full cost is confirmed in writing before the engagement begins, with no unapproved charges.
What happens after the final report?
Leadership can use the roadmap internally, work with the existing MSP, ask Stygian to scope a focused remediation sprint, proceed to a specialist Entra or Copilot review, or defer action. Where ongoing oversight is required, a managed Microsoft 365 security retainer can be considered separately.
Any Questions You Want to Ask?
Have questions about the Microsoft 365 Security Baseline Review, access requirements or whether the service fits your current concern? Speak to Stygian before committing to a wider audit or remediation programme.
Turn Microsoft 365 security uncertainty into a practical priority
Before adding more users, licences, external collaboration or AI capabilities, establish where the material control gaps sit and what should happen first. Stygian provides a focused, independent review so leadership can prioritise action with a clear evidence base.
Know what is exposed, what matters most and what to fix first
Book a 30-minute qualification call to confirm whether the Microsoft 365 Security Baseline Review is the right starting point for your organisation.
Blogs and Insights
AI Assurance Shouldn’t Be a Final Gate
The UK’s new AI Risk Management Toolkit points towards a better model: continuous AI assurance tied to services, architecture and real-world outcomes.
Legacy Is a Risk Problem, Not an Age Problem
GDS is rethinking the Service Standard around whole services. That should change how architects think about technology, operations and service outcomes.
Good Services Don’t End at the Digital Boundary
GDS is rethinking the Service Standard around whole services. That should change how architects think about technology, operations and service outcomes.